Malware & Ransomware
What Is SEO Poisoning: How Search Manipulation Targets Your Business
SEO poisoning redirects users from legitimate search results to malware-hosting pages, bypassing browser warnings through trusted search engine referrals.
SEO poisoning redirects users from legitimate search results to malware-hosting pages, bypassing browser warnings through trusted search engine referrals.
Volatile memory holds active encryption keys and hidden processes that disk scans miss, revealing the true state of a compromised system before it disappears.
Security groups act as stateful firewalls that automatically track return traffic, reducing configuration errors while creating hidden blind spots for lateral movement.
Most endpoint telemetry fails because it captures too much noise, masking the few signals that actually indicate an active intrusion attempt.
Tactical threat intelligence converts raw network noise into specific defensive actions by linking technical artifacts to active adversary behaviors.
SIEM systems aggregate data to reveal hidden patterns, but they generate noise that requires significant manual tuning to produce actionable security insights.
Voice-based social engineering often bypasses modern email filtering tools and exploits human trust more effectively than text messages.
Most organizations focus on user training, but the real defense lies in breaking the attacker's chain of command by isolating credentials and validating email paths.
Deception technology turns your entire network into a trap, ensuring that any interaction with a fake asset proves an intrusion has occurred.
Training alone cannot stop attacks because humans are not the weakest link; technical controls and system design determine your actual security posture.
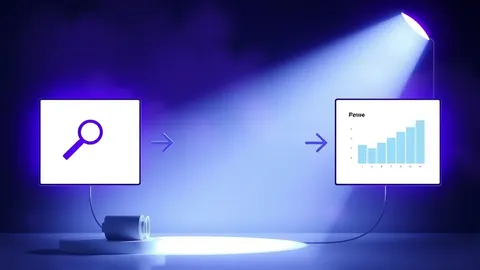
The intelligence cycle transforms raw data into actionable security decisions through a continuous loop of planning, collection, and analysis rather than a one-time report.
Third-party software dependencies create hidden entry points that bypass perimeter defenses and require continuous verification of integrity.
Stolen session cookies grant attackers immediate access to your accounts, bypassing multi-factor authentication and password protections entirely.
Rate limiting blocks volume but misses logic flaws, so you must validate every input to stop attackers from manipulating business rules.
Treating all automated traffic as uniform noise creates blind spots that allow credential stuffing and resource exhaustion attacks to bypass standard perimeter defenses.
Ephemeral infrastructure shifts security from static patching to automated verification, requiring you to trust code over human memory.
Attackers infect trusted industry sites to compromise visitors, turning your routine research into a direct pipeline for malware and credential theft.
Temporary controls buy time against exploitation while permanent fixes are developed, preventing immediate data loss without requiring full system rebuilds.
Automatic plugin updates reduce exposure to known vulnerabilities but introduce the risk of breaking site functionality if compatibility checks are skipped.
Hard-coded credentials survive source code rotation and deployment cycles, creating a persistent backdoor that automated scanners often miss until an attacker exploits the static secret.
Open redirects rarely cause direct data theft, but they enable credential harvesting attacks that bypass traditional security controls by exploiting user trust in known domains.
A responsible disclosure program turns security researchers into unpaid auditors, but only if you define clear rules for reporting and fix issues before they become public exploits.
Tax identity theft often occurs before you file, meaning your clean status with the revenue agency is the primary defense against lost refunds.
Typosquatting exploits human muscle memory to redirect traffic to malicious sites that mimic trusted services without triggering traditional security alerts.