Malware & Ransomware
How to Implement Offline Backups: Air-Gapped Storage Protocol
True offline backups require physical disconnection from your network to prevent ransomware from encrypting or deleting your only recovery copies.
True offline backups require physical disconnection from your network to prevent ransomware from encrypting or deleting your only recovery copies.
Attackers often exfiltrate data silently before launching ransomware, meaning early detection relies on spotting unusual outbound traffic rather than waiting for an encryption notice.
Most organizations collect logs but fail to normalize them, creating blind spots that attackers exploit to move laterally without triggering any automated alerts.
Static file analysis fails to detect dormant threats, making behavioral sandboxing and execution control the primary defense against modern payload delivery.
Most incident response failures occur because responders alter the very data they need to prove what happened, turning a recoverable incident into an unrecoverable liability.
Hardcoded credentials in public repositories remain a persistent risk because automated scanners often miss context-specific tokens that appear valid to the system.
Most failures occur because teams collect logs before defining the specific security events they intend to detect and respond to.
Most patches waste time because teams fix low-risk flaws first; context determines which holes actually endanger your business.
Modern intrusion prevention systems automate threat blocking at the network edge, reducing the need for manual log review while introducing configuration risks that require expert tuning to avoid disrupting legitimate business traffic.
Treating all software flaws as equal threats creates false urgency and leaves the most dangerous entry points exposed to exploitation.
Parameterized queries separate code from data by forcing the database to treat user input as literal values, making it impossible for an attacker to inject malicious commands.
Client-side validation disappears when an attacker sends a request directly to your server, making backend verification the only reliable defense.
Most attackers reuse network components across campaigns, allowing you to trace a single suspicious link back to a broader operation before damage occurs.
Defaulting to broad permissions creates a persistent attack surface that grows silently as staff turnover increases and systems evolve.
Defining who controls data and who processes it shifts liability, forces stricter vendor vetting, and prevents silent data leakage that standard contracts miss.
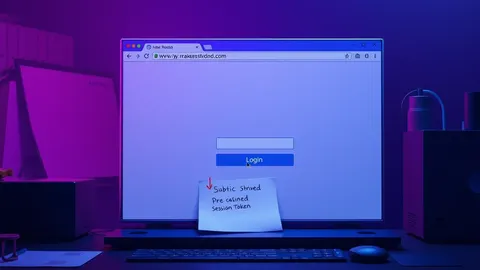
Attackers can force you to use a pre-set identifier, allowing them to enter your account the moment you log in without knowing your password.
Packers compress legitimate code to save space, while crypters encrypt payloads to hide malicious intent, yet both bypass signature-based detection.
Attackers exploit standard Windows search order behaviors to inject code, leaving traces in file timestamps and process ancestry that standard scanners often miss.
Most breaches succeed because attackers operate silently for months, exploiting the gap between entry and detection to move laterally and exfiltrate data.
Data masking creates a functional replica of your database that preserves structure while permanently removing the ability to identify specific individuals or accounts.
CSPM audits static configurations while CNAPP integrates runtime protection and development workflows to close security gaps before deployment.
You do not need to own the main domain to seize control of its subdomains, and passive monitoring often misses these silent takeover opportunities entirely.
You can validate your security controls without hiring a dedicated offensive team by using structured, hypothesis-driven testing cycles.
The most damaging action during an invoice fraud incident is replying to the attacker, which confirms your contact information is active and invites further targeted attacks.