Threat Intelligence
SIEM Benefits and Limitations: When Security Monitoring Pays Off
SIEM systems aggregate data to reveal hidden patterns, but they generate noise that requires significant manual tuning to produce actionable security insights.
Everything SecOps Signal has reported about log analysis: 4 stories, newest first. Part of our Threat Intelligence coverage.
SIEM systems aggregate data to reveal hidden patterns, but they generate noise that requires significant manual tuning to produce actionable security insights.
Scanning a code bypasses URL inspection, allowing attackers to redirect users to credential theft sites before security filters can react.
Credential stuffing attacks often bypass traditional alerts by mimicking legitimate user behavior patterns and timing, requiring deep log correlation to uncover.
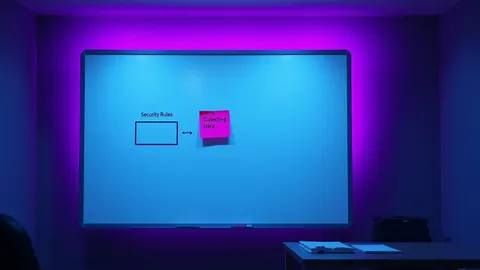
Most failures occur because teams collect logs before defining the specific security events they intend to detect and respond to.